


HIPAA-Compliant Chat API for Healthcare Apps
Build secure patient-doctor messaging and AI assistants with a HIPAA-compliant chat API designed for sensitive healthcare communication. Ethora provides the messaging infrastructure, SDKs, security controls, audit trails, and deployment options to build HIPAA-ready chat into web, iOS, and Android apps, without building real-time messaging from scratch.
What is a HIPAA-compliant chat API
HIPAA readiness is an architecture, not a single feature
A HIPAA chat API is a secure chat backend for building text, voice, or video into a healthcare application. Compliance comes from a combination of controls, not one checkbox. Ethora is designed to address these requirements while giving your team control over how the system is deployed and operated.
Encryption in transit and at rest
TLS protects PHI while it is transmitted; AES-256 protects it while stored. Encryption is one part of a broader security architecture, evaluated together with access controls, authentication, and auditability.
Access control by role
Patients, physicians, nurses, care coordinators, and admins should not all see the same conversations. Ethora supports authentication integrations and role-based access so messaging fits your existing identity and authorization model.
Audit trails
Maintain an auditable record of messaging and system activity, with retention you configure to meet your requirement (for example, a 6-year record). Useful for patient-provider communication, document exchange, administrative actions, and compliance reviews.
Business Associate Agreement (BAA)
When a provider handles PHI on behalf of a covered entity, a BAA is required. Ethora signs a BAA on every covered deployment: self-hosted Enterprise, a dedicated server (including Private Practice) or an Ethora Cloud account with HIPAA enabled on request. The template is published at /legal/business-associate-agreement/.
Data ownership
Keep PHI inside your own walls
The more control you have over the environment that processes healthcare data, the more control you have over its security, access policies, and data location. Ethora can run on your own infrastructure (AWS, Azure, GCP, or on-premises), or as a dedicated single-tenant cloud with Enterprise support and a BAA.
You control where PHI lives
Data location, network configuration, infrastructure access, storage and backups, monitoring, and deployment region.
Runs in your environment
Your messaging infrastructure operates within the same controlled environment as the rest of your healthcare application.
Or fully managed
Prefer to not run it yourself? A dedicated, single-tenant cloud deployment gives you an isolated managed environment with Enterprise support and a BAA.
One API, every platform
Drop in the SDK and open a secure conversation
The same backend powers messaging across Web (React), iOS (Swift), Android (Kotlin), and React Native. A patient can message from a mobile app while a clinician manages the same conversation from a desktop interface.
const chat = new EthoraChat({
  apiUrl: YOUR_HOST,
  appId: YOUR_APP_ID
});

await chat.login(userToken);

const room = await chat.rooms.create({
  name: "Care team - Jane D."
});

await room.send({
  text: "Labs are back and look good."
});
Example integration. React, React Native, iOS (Swift), Android (Kotlin), Node.js, and Python are supported.
AI in healthcare communication
Add AI assistants to patient and clinical workflows
Use cases
Where teams use a HIPAA-compliant chat API
Patient portals
Give patients a secure way to reach doctors, nurses, and staff from the patient portal.
Telehealth apps
Add secure messaging before, during, and after a virtual appointment, with file and image sharing.
Clinical collaboration
A dedicated communication layer for authorized clinicians and staff, with access controls and audit history.
Care coordination
Connect authorized care-team members across organizations, keeping conversations, files, and history in one controlled place.
Build vs buy
HIPAA chat API vs building messaging from scratch
Building internally gives maximum control, but your team becomes responsible for every part of the communication stack.
Custom build
Ethora SDK
Compliance documents
Read the agreement and the checklist before you talk to us
Both are public. The BAA is the one we sign; the configuration guide is what your admin applies before PHI goes in, on any of the three covered deployments.
Business Associate Agreement
The HIPAA BAA Ethora signs on self-hosted Enterprise, dedicated and HIPAA-enabled cloud deployments, with the sub-processor list and the allocation of safeguards.
Read the BAAHIPAA configuration guide
Ten settings in order: MFA for admins, registration off, generic push content, encryption and encrypted rooms, immutable audit export, AI and translation, webhooks, widgets, analytics, people and devices.
Open the guideEnable HIPAA on your cloud account
Most HIPAA customers self-host, but the shared cloud works too: email support to enable HIPAA for your account or to get a trial dedicated server in your region.
Email supportCase studies: HIPAA-compliant chat
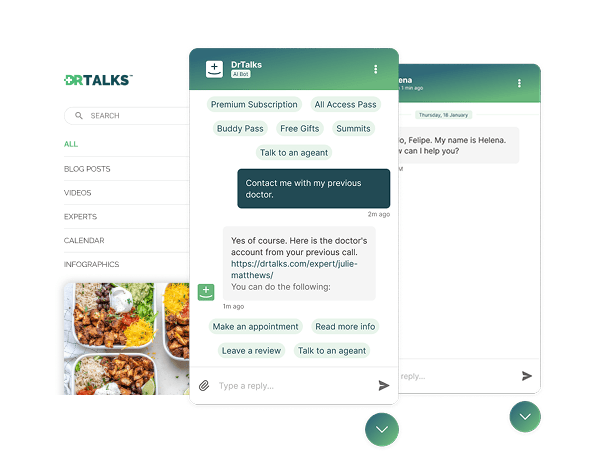

Healthcare: HIPAA-compliant AI assistant (RAG) over a medical video library
Dr. Talks is one of the most prominent organizers of online healthcare conferences and summits.
Ethora enabled them to create a context-aware AI-powered chatbot to help users navigate thousands of pages of medical content, correctly referencing pages, authors, videos and timestamps. 100% secure and HIPAA-compliant.
This assistant enhances user experience by simplifying interaction with the platform and reducing search time.
- 1000+ summits indexed by AI bot
- Instant user engagement
- Vector embeddings enable intelligent domain expert AI responses
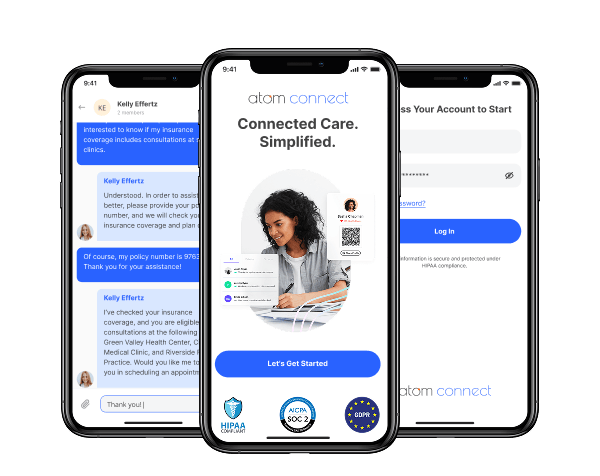

Insurance: in-app chat for a workers’ comp health insurance provider (HIPAA compliant)
Atom Advantage provides workers’ compensation and health insurance solutions in the United States.
On Ethora they built Atom Connect: secure, case-based chat between injured workers, nurses and case managers, embedded in their claims portal and a white-label mobile app. HIPAA and SOC 2 compatible.
Less manual work for case managers and a better experience for injured workers.
- Chat embedded in the case managers’ web portal
- White-label iOS and Android app for injured workers
- One secure room per claim, created automatically by API

Healthcare: self-hosted patient messaging for a multi-clinic digital health platform in Canada
VITALL is a Canadian digital health platform used by hospitals, clinics and private practices.
Ethora runs as a self-hosted chat server in VITALL’s own AWS account in Canada, with one isolated tenant per clinic, chat in the practitioner portal and in native iOS, Android and React Native patient apps.
Users, rooms and clinics are provisioned by VITALL’s backend through the Ethora API.
- Self-hosted in the customer’s AWS account in Canada
- One isolated tenant per clinic, created by API
- Web portal, iOS, Android and React Native SDKs
HIPAA chat API FAQ
Does a HIPAA-compliant chat API require a BAA?
If your service provider acts as a business associate and handles PHI on your behalf, a BAA is required. Ethora signs one for every covered deployment; the template is published at /legal/business-associate-agreement/ so your compliance team can read it first. Your legal or compliance team determines whether your specific use involves PHI.
Can I add a HIPAA compliant AI chatbot as well?
Yes. The same platform runs AI agents that answer from your own content, on your website, in your patient portal or alongside your staff. For PHI, run them on a dedicated or self-hosted deployment with a BAA and a self-hosted model or a model provider under its own BAA. See the HIPAA compliant chatbot page.
Do you sign a BAA?
Yes. Ethora signs its Business Associate Agreement with every customer on a covered deployment: a self-hosted Enterprise server, a dedicated server we run for you (including the Private Practice server), or an Ethora Cloud account with HIPAA enabled. Most HIPAA customers self-host, but you do not have to: get in touch with tech support to enable HIPAA for your cloud account or to get a trial dedicated server. The settings you apply before PHI goes in are in the HIPAA configuration guide.
Can I self-host so PHI never leaves my network?
Yes. Ethora supports self-hosted deployments on AWS, Azure, GCP, or on-premises infrastructure, giving you control over data location, infrastructure access, network configuration, and security policies. On a self-hosted server no Ethora sub-processor holds PHI at all. The configuration guide lists what you set up on your side (TLS, encrypted volumes, the immutable audit log export) and what is in the software already.
Is regular chat or SMS HIPAA compliant?
Consumer messaging apps and standard SMS are not inherently HIPAA-compliant. Healthcare messaging needs access control, security, auditability, and the relevant contractual safeguards. A healthcare messaging API provides the framework to implement those; SMS and consumer messengers usually do not.
Is encryption required by HIPAA?
HIPAA does not mandate one specific encryption technology for every implementation. Encryption is an important safeguard, but compliance depends on the complete set of technical, physical, and administrative safeguards your organization implements. Ethora encrypts PHI in transit (TLS 1.2+) and at rest (AES-256). End-to-end encrypted rooms are available as an opt-in per app; most covered entities keep them off, because an encrypted room cannot be archived, searched, or moderated on the server.
Can I integrate a HIPAA chat API into an existing application?
Yes. Ethora integrates into existing applications and supports web and mobile development, including React, React Native, iOS, and Android.
What is the difference between a HIPAA chat API and a HIPAA chat SDK?
A chat API is the backend interface (typically REST + WebSockets) for messaging functions and compliance features; you still build the UX and client logic. A chat SDK is a ready-to-use toolkit with pre-built methods and UI components so developers ship faster. Ethora provides both the SDK components and the API/backend.
What platforms does Ethora support?
Web (React), iOS (Swift), Android (Kotlin), and React Native. The same backend powers conversations across every client.
How long does integration usually take?
Most teams get a working version in a few days. A production integration typically lands within one to two weeks, depending on the complexity of the surrounding systems.
Build a HIPAA-compliant chat experience
Get a chat and messaging API with encryption in transit and at rest, a signed BAA, audit trails, and a self-hosting option. Talk to our team about your healthcare communication and compliance requirements.
